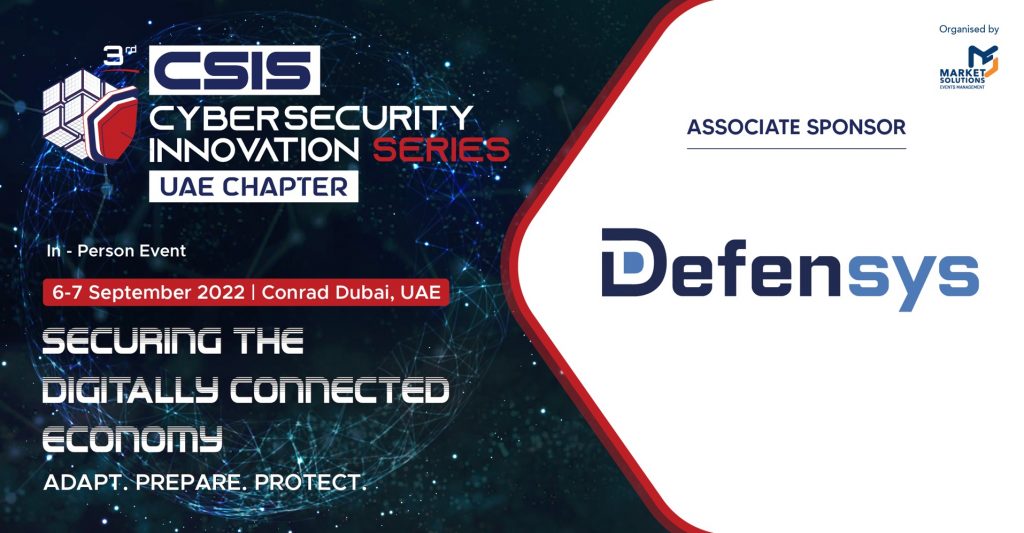
On the 6th and 7th of September in Dubai, UAE there will be held the third annual conference dedicated to cyber security innovations – CSIS 2022 and the Defensys company is a partner of this respectful conference.

CSIS aggregates professionals in the area of IT and cybersecurity for the exchange of experience and competencies in order to counter the problems that companies from all over the world face on a daily basis: the growth of cyberattacks, data leaks, security problems related to cloud technologies etc. The main discussions will focus on artificial intelligence, machine learning, cybersecurity regulation and, of course, high-tech solutions for infrastructure protection. This conference is designed to help various businesses and governments maintain resilience and adapt to the ever-changing methods of cyberattacks.
Challenge

This is CERT, which main task is to collect information about incidents from its subordinates , as well as inform them about the main threats, attacks, vulnerabilities etc.

Before taking a look at the SOAR class systems almost all the procedures of interacting with different representatives of the regulated companies were manual. CERT communicated
with everyone via mailbox. For manual enrichment of IoCs delivered from subordinates, CERT analysts used various services, for example, WHOIS.

Also there was a demand from the regulated companies to have an electronic service to operate with this CERT with the possibility to automatically register incidents and IoCs.

Defensys products

The customer wanted to estimate comprehensively different types of building automation for their needs covered above:

  • matured software from some vendor with features specially tailored for such needs
  • ServiceDesk-like systems with some added programming and customization
  • fully custom programmed software based just on the needs of this CERT

As a result a part of Defensys’s ecosystem: SOAR + TIP was chosen among other respectful vendors for building this selfservice cybersecurity portal.

Results

The following number of important issues was resolved after the implementation of Defensys SOAR+TIP:

Challenge

The customer had some number of implemented systems not integrated between each other among them that logically caused frequent problems.

Moreover, there were 3 main types of information that were processed in the company:

  • Data on critical information infrastructure (CII) objects. During
    the work on the project, Defensys’s engineers along with
    colleagues from the partner’s side imported all CII objects into
    the Defensys SGRC and updated them
  • Trade secret type
  • “For internal use” type of Information

All cyber security audits were carried out in 3 areas:

  1. CII
  2. Trade secret
  3. Compliance with internal checklists

The hard challenge to find the right solution which could be flexible in settings and integrations and solve collected problems was set by the customer. After a careful search, the company has chosen Defensys SGRC solution.

Results

First of all, regulatory and physical security requirements were fetched between each other via control checks framework built in Defensys SGRC. This way the user receives only one list with all the requirements needed to be assessed depending on the type of an asset and his role in the process (not all the requirements).

Effective exchange of information about threats among multiple participants works like collective immunity: the more participants are involved in this process, the higher the probability of successfully resisting the attackers. We will tell you in the article about the culture of sharing such data and what are the main pitfalls of this area.

What is data exchange culture, and why is it needed?

It is worth exchanging information about threats for at least three reasons. Firstly, to save money, because it is cheaper to prevent an attack than to eliminate damage from it. Secondly, to be socially responsible: to fight together with other companies against a common enemy. Finally, thirdly, to have a good reputation. A company is trusted not only by customers but also by investors if it is conditionally safe.

To date, it is possible to distinguish several types of data shared by TI exchange participants:

According to the 2021 SANS Cyber Threat Intelligence (CTI) Survey, 66.3% of companies use open sources to collect indicators of compromise and try to work with multiple sources simultaneously. It would seem that collecting indicators from open sources is a fairly simple task: you just need to download a txt or csv file from some web-site, and that’s it. In fact, there are many problems along this way. In this article, we will tell you what these difficulties can be, what the structure and format of the feed depend on, what metrics help to evaluate the usefulness of feeds, and also show what you can learn from the feed using a real example.

What are the pitfalls of open source TI

Let’s make a reservation right from the beginning: you cannot bypass problems when you are working with indicators from open sources. At the first loading of such indicators into security tools, you will receive thousands of positives per day. If you don’t even analyze the first 100 hits, you will most likely spit on this issue and just turn off the feed.

Let’s try to describe the main problems that will need to be resolved when collecting indicators from open sources:

Challenge

Each of the company’s subsidiaries and branches has its own IT and OT networks.

The OT Cyber security department’s main desire was to aggregate data on OT assets in one place because standing on this up-to-date data they could proceed with different compliance procedures: national and internal.

Inventory data was stored in absolutely different places:

  • Industrial IDS and AV system databases
  • Custom databases
  • Electronic documents
  • Paper documents etc

There was also one more complicated thing in this distributed chain of tenants – a lot of them were built based on one standard project, that’s why there were a lot of different subnets with the same addresses.

Colleagues felt the need for automation because it wasn’t at all efficient to try to gather all the information by email.

Results

After the PoC process, the Defensys SGRC solution was selected to close all the objectives.

The system works in multitenancy mode. With this functionality, all assets can be stored in the same location for future use in other cybersecurity processes, regardless of whether they have the same addresses.

All the inventory data from the sources described above is merged into specially designed asset cards forming the unified resource-service model of the OT part of the company.

The Defensys company has released a new version of its platform for automating cyber security management processes – Defensys SGRC 5.0. In this version vendor enhanced compliance, asset and vulnerability management features.

A lot of new regulatory standards strongly affect the system’s development. For instance, SAMA framework that was recently added to the Platform demands new reporting templates and assessment scales. The same thing is with GDPR, UAE IA Regulation framework and some other standards including in-house frameworks from customers that sometimes demand different mathematics to calculate resulting indexes after the audit is completed.

That’s why in Defensys SGRC 5.0 there appeared an “import/export” feature for audit types. The type affects what scale will be used for the assessment, what fields will be available for the filling and how will be statistics calculated. This feature significantly helps to quickly transfer all the needed preferences from the testing segment/installation to the productive server during the specific stage of some implementation project.

Challenge

The Computer Security Incident Response Team of MSSP, was facing a typical for a MSSP challenge of choosing the right SOAR platform for automation of their internal incident management processes.

Key Requirements

While choosing the product the company looked at several criteria with the following key requirements:

  • MSSP-ready product with all necessary functions in place for delivering high-speed incident response service
  • High quality and reliability
  • Minimum resources required for product maintenance
    and support
  • A mature development team and responsive first line
    technical support helping to adapt the product to their
    needs

The managed security service provider team selected 6 SOAR products for initial comparison 4 of which were tested during the pilot projects.

After comparative analysis and testing, the team selected Defensys SOAR platform.

The specifics of the MSSP

The MSSP has 3 Tiers for incident monitoring working 24/7 with separate response and maintenance groups, forensic, threat hunting and other experts. The whole team follows one single integrated workflow that regulates the incident management process and specifies tasks for each team member at certain stage. This automated workflow includes 140 playbooks covering more than 100 scenarios of threat
detection.

Threat Intelligence (TI) platforms work with knowledge about cyber security threats: attacks, attackers, targets, motivations, tools, malware, vulnerabilities and indicators of compromise. This knowledge must be fact-based – verified, timely, and sufficient to make decisions on adequate protection measures.

In a general sense, an Indicator of Compromise (IoC) is a digital artifact that clearly indicates the described object’s potential maliciousness and/or the fact that the information system has been compromised.

In the process of working with TI data, the following indicator types can be used as:

  • IP addresses
  • domains
  • files
  • links
  • hash sums of files
  • email addresses
  • bank cards
  • accounts

The life cycle of an indicator of compromise

Each indicator has its life cycle, i.e. the time during which it preserves its malicious activity with a high probability. Some indicators can be “dangerous” for several days, some – for months. When its lifetime expires, the indicator becomes irrelevant, in other words, it becomes obsolete.

Challenge

The Bank combines a variety of solutions and services for collection and analysis of cybersecurity alerts. To make the incident response process more efficient the bank needed an advanced tool which would allow to relate incident alerts to assets and users, automatically assign tasks to members of the cybersecurity department team, automatically collect context and additional data from multiple sources and automate security operations. The implemented automation had to accelerate incident response and help to minimize the potential damage to the bank.

Key Requirements

  • Incident response automation
  • Automated collection of additional information
  • Automated task assignment and management for the employees
  • Automated vulnerability management process

Defensys products

PoC for Defensys SOAR lasted for a quite long time comparing to the average period of testing Defensys products and proved all the features of the cybersecurity management platform which combines Defensys SOAR and Defensys SGRC products to cope with the tasks.

All critical assets were discovered and structured in the Defensys platform during the testing period. Tight integration with security tools in use and external monitoring services was configured.