Introduction

Many articles have been written about Deception. It is not surprising as deceptive technologies have been taking over the cyber security world in recent years. In the recent Gartner report Deception was named as one of the most effective information security technologies: according to experts, it is almost at its peak and is expected to reach the plateau in the horizon of 5-10 years. We decided to fantasize about what it would be like if there was some “ideal solution” in the market that combines all the features of modern cyber deception technologies.

In this series of articles, we have compiled a summary list of Deception’s features present in these or those solutions. And here we will not go into technical details, our goal is to help readers take a broader look at cyber deception technologies and their possibilities, especially in terms of a defensive strategy, and choose their own “golden standard” for themselves.

Architecture and delivery options

Let us start with the basics: the architecture and possible product delivery options. Architecturally, Deception solutions traditionally fall into several classes:
Cybersecurity news

Challenge

Most of the SOC analysts’ time was spent daily for manual prioritizing security alerts from the SIEM and then for manually generating IT tickets in SD. Between these two big processes were chaotic enquiries for colleagues to find out what equipment was involved in incidents and numerous attempts to reactively respond to these incidents.

There literally was no time for something else in terms of cybersecurity needs of the Organization.

When a new organization wanted to use SOC services, all the generated data during this process was stored in different shared folders and electronic documents. It was a great challenge to combine the whole picture of how the interaction with this specific organization was handled. Plus, there was a demand to keep the control not only of IT assets, but also cameras, physical control points, USB tokens and fetch them with the IT asset model.

Results

There is a structure of playbooks designed for every type of registered incidents and implemented in SOAR. All the correlation rules of the SIEM alert to the SOAR, where everything is instantly mapped and labeled with MITRE ATT&ACK tactics and technics.

There is a main playbook that contains subplaybooks that are launched depending on the conditions that are gathered during the playbook execution.

Cybersecurity news

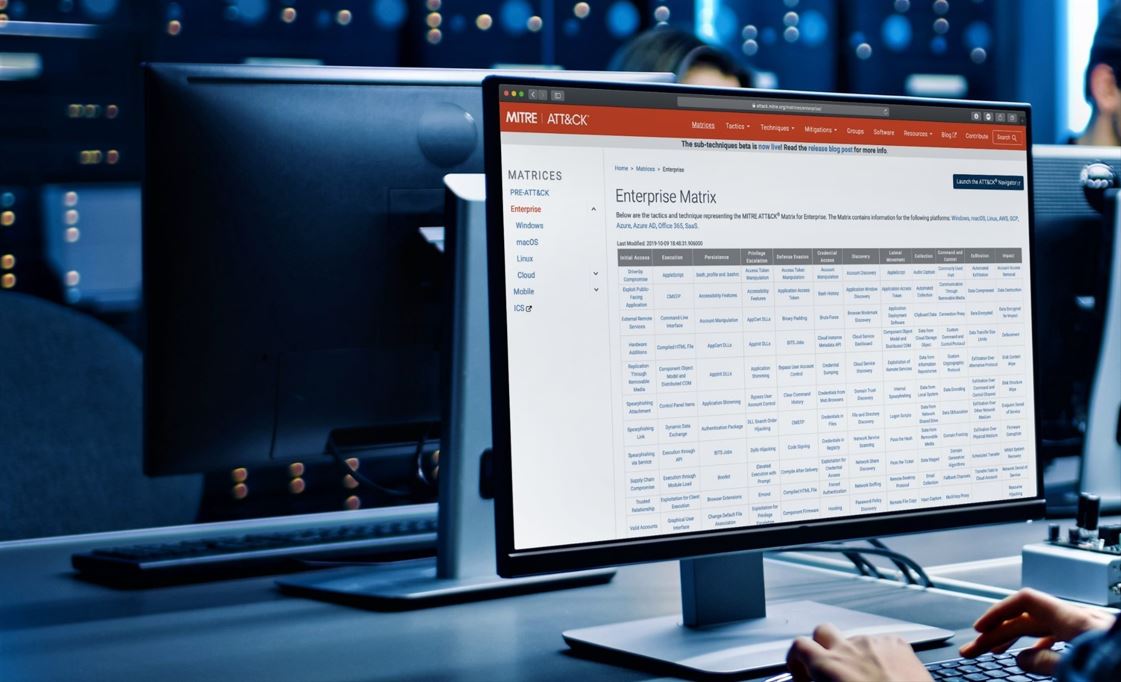
Our colleagues from the Center of expertise at Defensys use MITRE quite often during our PoC and implementation projects. And we would like to share our thoughts about these very MITRE matrices and their application in this article.

Recently, we hear more and more often that developers actively use MITRE methodology when developing various cyber security products. In MITRE terms, these databases are called matrices, and the number of projects where they are used is constantly growing.

At the same time, we have been wondering for quite a long time now: what does MITRE support give to vendors and end users in the end? Why do we need it all, if we already have, say, some kind of “smart” SIEM or a specialist who constantly works with it?

Our article is designed to get to the bottom of these questions. And to begin with, we suggest to remember what MITREs are.

MITRE is an American non-profit organization that manages systems engineering research and development centers at the U.S. federal government and local government levels.

And then there’s MITRE, a manufacturer of sports equipment.

What is MITRE famous for?

MITRE ATT&CK

Today we’re going to tell you about the analytical features of Defensys SENSE – the core functional part of this security analytics platform which main aim is to detect security violations in the infrastructure, different anomalies, suspicious activity and to do the dynamic security scoring of all the objects related to your logs.

Defensys SENSE provides a comprehensive approach for the security events analysis when it studies objects (and similar groups of objects) behaviors, forms normal behavior patterns and detects suspicious activities when they don’t match these patterns.

This qualitative analysis is performed by using 2 types of instruments: simple rules and programmatic experts.

Simple rules

Simple rules is a basic mean to analyze security events and its main feature is a very easy tuning.

Information systems analysts can quickly tune the current rules of create their own ones. When you create a new rule it’s enough to just add criteria for events filtering and as a result all the found events will be marked as suspicious and related observation objects will collect some new number of threat points. Defensys works with the following observation objects: hosts, accounts and users. The overall threat points are aggregated for all the objects that come from logs.

Scoring is the mean to evaluate objects’ anomalies and the potential impact that can occur if this anomaly will become a threat.

Challenge

Initially, the incident response process was conducted by the SIEM system. The customer had about 7 instructions for different types of incidents with a brief description of what needs to be done in such situations. Also, colleagues did not have a response process. Security specialists used to look at the screen, and if they saw the incident in the SIEM they started working with it according to the instructions. If the incident was something not common, then it was processed randomly.

The Defensys company issues a new version of its platform for digital imitation of IT infrastructure elements Defensys Threat Deception Platform (TDP) v. 1.5. It has the expanded list of traps and lures templates, integration with the SOAR system from Defensys and the enhanced capabilities of working with security events.

In the Defensys TDP v. 1.5 vendor has complemented the list of traps and lures templates. There appeared HTTP traps, that imitate logon screens of network equipment and also lures for MacOS and Linux operating systems. One more new thing – lures for saved connections to SMB network sources.

One more significant new feature is related to the integration capabilities. Besides a standard syslog push integration with external systems Defensys TDP now has direct seamless integration with the Security Orchestration Automation and Response system Defensys SOAR. Now all the events related to the same trap detected by Defensys TDP are automatically transferred to the Defensys SOAR in a form of one aggregated incident. Furthermore, a user can manually tune a period of aggregating of these events from the required trap.

From time to time when researching product ideas and hypotheses, our team develops prototypes. We have an opinion that some of them could be useful to the cybersecurity community. Today we want to share a model for ranking indicators of compromise that we implemented based on the study “Scoring model for IoCs by combining open intelligence feeds to reduce false positives” by the University of Amsterdam. This model solves one of the key tasks of threat intelligence: ranking indicators of compromise according to a number of parameters in order to distinguish among them the most dangerous and narrow the focus of the search for threats.

The model operates with sufficiently clear parameters (coefficients), which are used in the calculation:

Defensys is proud to announce that current version of the SGRC now supports Shariah Governance Framework for Local Banks Operating in Saudi Arabia.

This framework is ready to be used in compliance procedures by all the organisations operating under the requirements regulated by SAMA along with the SAMA frameworks themselves.

“We rapidly responded on such a demand from mostly banks in the KSA where we currently doing projects with our partners. Now any institution that operates in the Kingdom can do all the audits using out-of-the box frameworks available right after the installation of our SGRC solution which is a part of the whole cyber security ecosystem by Defensys. Also there is an option to add local and internal frameworks, standards and check-lists fetching all the requirements into the one list to save time of our customers when assessing similar requirements from different standards”

The Defensys SGRC solution helps enterprise companies of different scales to control the state of cybersecurity and effectively evolve cybersecurity based not only on compliance procedures but also on automatic risk assessments and the ability of the system to merge all the needed inventory data from different sources to create a master assets source for the whole organisation.

As usual Defensys’s cyber security experts are ready to share all the trendy approaches to maximize the effect of the SGRC implementation.