Challenge

The Factory has purchased step by step all Defensys products: SOAR, Security GRC, Threat Intelligence, SENSE and Threat Deception platforms. As a part of large project on software installation and customization, our target was to build an ecosystem based on Defensys software which will cover all cybersecurity needs of the factory.

Implementation

Since each company has its own internal procedures, Defensys takes into account all customer requests and adapts software to specific requirements. The factory has 5 types of incidents to be detected, so there were tailored 5 SOAR playbooks that utilize different connectors during the response and investigation processes.

The company stored most of the assets data in a SIEM system and all incidents for further processing are being taken from the SIEM too. Besides, it’s connected with AD and antivirus solution.

At the moment, by using Defensys software, the company can do the following:
Defensys developed an updated Platform for assets behavior analysis and anomaly detection, the Defensys SENSE v. 1.14. The Platform now can be integrated with the Defensys Endpoint technology, which extends the function of endpoint data collection. The new Platform version provides cyber security analysts with more context while looking for the causes of anomalies due to the modified asset card.

With the new version, users get access to a wider range of events and telemetry from different operating systems, including Windows, Linux, and MacOS. This expands the data flow from endpoints, which delivers CS analysts incidents of higher quality for the following assessment. This process was implemented thanks to integration of the Defensys SENSE with the Defensys Endpoint technology.

The asset card was significantly updated. At the moment asset’s technical data and related entities are displayed on the asset card besides the basic information. Because of this, users can quickly access full context of the necessary asset and remarkably speed up the root cause search.

Therefore, Defensys added a new tab “Daily analytics” to the asset card, where you can find rating changes, anomalies, and involved equipment for the last 24 hours. After detection of equipment with a high rating, cyber analysts can research all users’ actions during the day with a single click and define, if investigation is needed in case of anomaly activities detection.

Cybersecurity news

Threats catalogs

There is a lot of discussion in the professional community about risk assessment methodologies. At the same time, much less attention is paid to a more powerful indicator of the maturity of the process – the process of building threats catalogs.

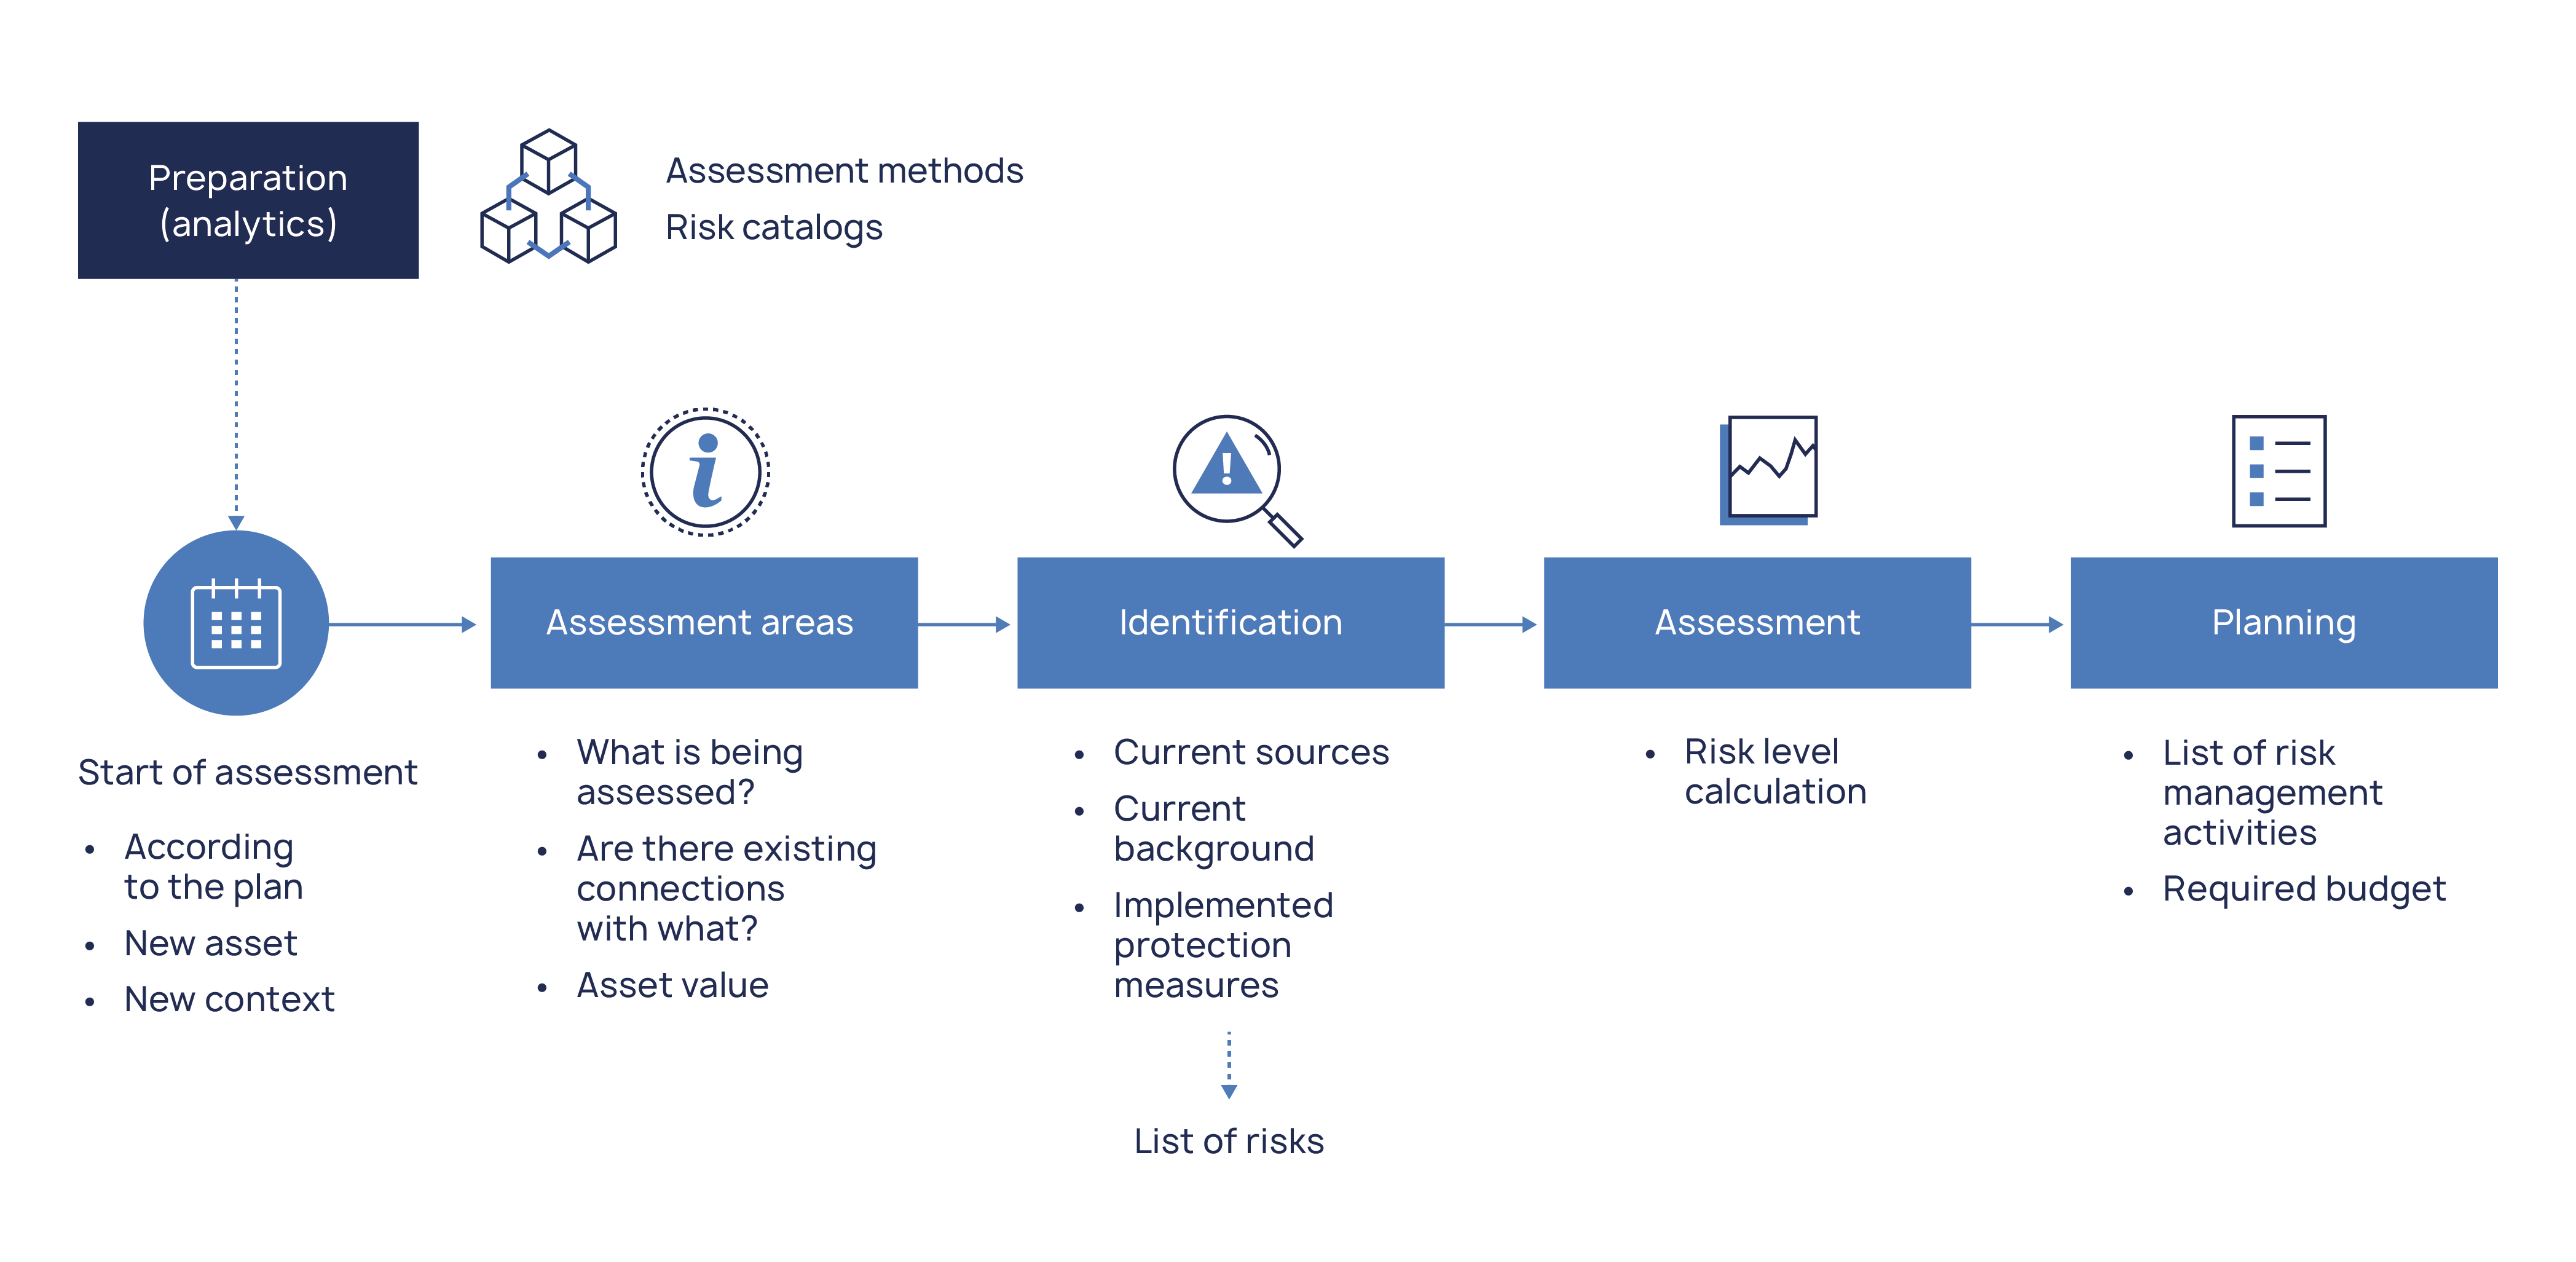
Let us turn to a typical assessment process:

Risc catalogs

After a one-time event – the preparation of methodological materials – the assessment cycle begins on a schedule or trigger. The first step is to determine the assessment areas, a step that depends largely on the completeness of the data on the resource-service model. As with audits, it is important here to see the connections between tangible and intangible assets.

The value of the asset, the most difficult step in terms of assessment, was discussed earlier.

The next step, i.e. identification, is the formation of a list of risks for further assessment. And it is this step that often becomes a stumbling block for inexperienced organizations.

Challenge & Implementation

One of the entity’s departments has already implemented Defensys SOAR and among all other useful features it has the aggregated assets model that SGRC uses via the integration with SOAR. With a rise of the total number of technical equiHaving experience with our software and trusting

Defensys as a reliable vendor, the organization purchased Defensys SGRC for the integration with their internal portal. This portal, created for governmental bodies, is a multifunctional tool for employees of different departments and organizations. Portal allows users to create requests with various purposes. The government entity plays here the managing and approving role.pment within the entity SOAR became increasingly important.

The main function of SGRC in the organization is to automatically fetch all the received requests with the asset model. Thanks to the role model of the SGRC all the necessary asset types can be owned and managed by certain number of employees. Access to a particular asset with all stored requests and created data may be shared between employees of one or several departments.

After receiving and approving portal requests, a new customized entity with a certain status is added to SGRC via API. This asset, depending on type, relates to a relevant asset group automatically.

Cybersecurity news

We are excited to announce the integration of the Defensys SOAR platform with ChatGPT from OpenAI. This integration brings a change to the way users interact with ChatGPT directly within the SOAR incident chat window. By eliminating the need for separate windows, it significantly reduces the time required to obtain relevant information while maintaining the context of the conversation.

But that’s not all.

With the integration of ChatGPT, real-time analysis of incoming incidents and their contextual information becomes possible. Leveraging the power of the MITRE ATT&CK framework, ChatGPT can identify attacker tactics, techniques, and sub-techniques. This enhanced visibility enables analysts to understand the current state of the attacker and anticipate the attacker’s next steps.

And there’s more.

Additionally, the integration empowers effortless generation of incident reports tailored to various stakeholders. Whether it’s a report for managers, directors, or customers, the integration allows for the creation of comprehensive reports in any desired format at the click of a button.

By leveraging ChatGPT’s capabilities, analysts can analyze the accuracy and precision of actions performed, receiving valuable recommendations and insights. ChatGPT assists in identifying any overlooked or undocumented details, providing hints to enhance the quality of incident response.

Defensys has updated the Platform for automation of information security management SGRC. Developer has reviewed the categorization process of сritical assets and taken into consideration new legislation regarding personal data processing.

In the 5.2 version of Defensys SGRC the list of criteria and values for assessing the category of critical assets has been updated. Due to this users now can determine the asset value more precisely and timely notify the regulatory authorities about the categorization.

Personal data processing procedure was also modified by the developer. The Platform enables users both to create and maintain up-to-date lists of information systems, business processes and responsible employees and to consider other assets involved in personal data processing. Users can automate routine tasks, such as notifications regarding personal data changes, damage reevaluation in case of law violations and changes in the composition of technical devices within the company infrastructure.

One more important update to the Platform is the extension of pre-installed methods supplied in the SGRC, which allow users to enter data on current tactics and techniques, as well as define security threat scenarios to form threat models as a part of a risk assessment approach.

Cybersecurity news

Defensys introduced a new major version of cyberthreat information analysis platform, the Defensys TIP 3.0. The updated platform has a number of significant functional improvements. In particular, users now can apply more qualitative data for threat analysis because of a new source – the MITRE ATT&CK knowledge base. The feature of the IoC rating customization is also available now.

In the Defensys TIP v. 3.0 the developer expanded the volume of cyber intelligence data by integrating the platform with a new source – the knowledge base MITRE ATT&CK. You can get information about malware, threat actors and their techniques directly from the platform interface in the Threats section. Entity cards contain all the information from the knowledge base: entity descriptions, related tactics, synonyms of groupings, sub-techniques, links to web resources that present cases where hackers use certain techniques, as well as recommendations for detecting them.